
CRA Authorised Representative:Roles, Responsibilities and Risks
What Manufacturers Need to Know About Appointing an Authorised Representative Under the EU Cyber Resilience Act
The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, introduces cybersecurity obligations for manufacturers of products with digital elements (PwDE) placed on the European Union market.
For manufacturers operating internationally, understanding the roles of different economic operators is an important part of preparing for CRA compliance.
One such role is the Authorised Representative (AR), which is addressed under Article 18 of the CRA.
Manufacturers may appoint an Authorised Representative through a written mandate to perform specific regulatory duties on their behalf. However, this appointment has clearly defined limitations.
Appointing an Authorised Representative does not transfer the manufacturer’s overall CRA compliance responsibilities.
Understanding this distinction is essential for manufacturers and organisations considering acting as an Authorised Representative.
1. What Is an Authorised Representative Under the CRA?
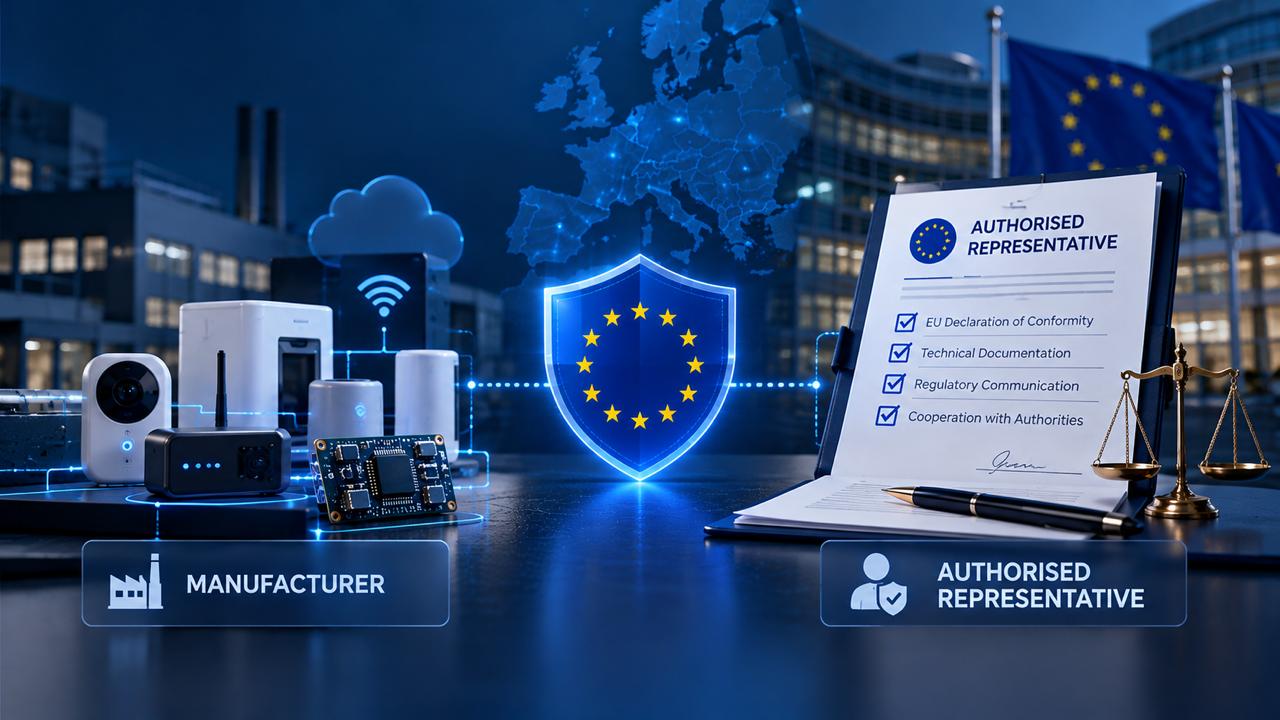
According to Article 18 of the Cyber Resilience Act, a manufacturer may appoint an Authorised Representative through a written mandate.
The Authorised Representative performs the tasks expressly assigned under that mandate, within the boundaries established by the regulation.
These tasks primarily concern regulatory documentation, communication with market surveillance authorities, and cooperation in addressing product-related risks.
However, the AR does not automatically become responsible for the product’s cybersecurity design, development, or overall regulatory conformity.
The CRA explicitly excludes certain manufacturer obligations from being delegated through an AR mandate.
Therefore, appointing an AR should be understood as establishing a defined regulatory representation arrangement, rather than transferring the manufacturer’s cybersecurity responsibilities.
2. Which Responsibilities Remain with the Manufacturer?
Article 18(2) establishes important limitations on the responsibilities that may be assigned to an Authorised Representative.
The obligations specified in Article 13(1)-(11), the first subparagraph of Article 13(12), and Article 13(14) cannot form part of the AR mandate.
These include fundamental manufacturer responsibilities relating to:
- Secure product design and development: Ensuring that products with digital elements meet applicable essential cybersecurity requirements.
- Cybersecurity risk assessment: Identifying, documenting, and addressing cybersecurity risks throughout the product lifecycle.
- Third-party component security: Exercising due diligence when integrating external software and hardware components.
- Vulnerability handling: Establishing appropriate processes for identifying, assessing, remediating, and managing vulnerabilities.
- Security maintenance: Managing cybersecurity requirements and security updates throughout the applicable support period.
- Conformity assessment: Fulfilling the manufacturer’s applicable obligations before placing products on the EU market.
- Ongoing product conformity: Maintaining appropriate procedures to ensure continued compliance as products and relevant requirements evolve.
An Authorised Representative may support regulatory coordination, but the manufacturer remains responsible for fulfilling these non-delegable obligations.
3. What Are the Authorised Representative’s Minimum Duties?
Article 18(3) establishes minimum tasks that must be covered by the written mandate.
Maintaining Regulatory Documentation
The Authorised Representative must keep the EU Declaration of Conformity and technical documentation available to market surveillance authorities.
These documents must remain available for at least 10 years after the product has been placed on the market, or for the applicable support period, whichever is longer.
Responding to Market Surveillance Authorities
Upon a reasoned request from a market surveillance authority, the AR must provide the information and documentation necessary to demonstrate the product’s conformity.
This requires reliable access to relevant technical information and an effective communication process with the manufacturer.
Cooperating on Risk Mitigation
When requested, the AR must cooperate with market surveillance authorities regarding actions intended to eliminate risks associated with products covered by its mandate.
Providing the Written Mandate
The AR must also provide a copy of its written mandate to market surveillance authorities upon request.
These responsibilities make documentation management, communication procedures, and clearly established contractual arrangements essential.
4. Why Is a Clearly Defined Written Mandate Important?
The written mandate is the foundation of the relationship between the manufacturer and the Authorised Representative.
An insufficiently defined mandate may create uncertainty about responsibilities, access to documentation, regulatory communication, and escalation procedures.
A well-structured mandate should clearly identify:
- The manufacturer and the Authorised Representative
- The products, models, or product families covered
- The responsibilities assigned under Article 18
- The documentation that the manufacturer must provide
- Procedures for responding to regulatory requests
- Communication and escalation responsibilities
- Effective date, duration, and termination conditions
The agreement should also explicitly acknowledge that the manufacturer’s non-delegable CRA obligations remain with the manufacturer.
Beyond the regulatory mandate itself, the parties should consider separate contractual provisions addressing confidentiality, liability allocation, legal costs, insurance, and termination rights.
A clearly defined mandate protects both parties by establishing operational expectations and reducing ambiguity.
5. What Are the Regulatory and Liability Risks?
Although an Authorised Representative is not responsible for guaranteeing the manufacturer’s overall product conformity, it remains accountable for fulfilling its own obligations under the CRA.
Article 64 establishes an administrative penalty framework for violations of specified regulatory obligations.
For infringements covered by Article 64(3), the regulation provides for administrative fines of up to:
EUR 10 million or 2% of the undertaking’s total worldwide annual turnover for the preceding financial year, whichever is higher.
Additionally, Article 64(4) establishes a penalty framework for providing incorrect, incomplete, or misleading information in response to requests from market surveillance authorities or notified bodies:
Up to EUR 5 million or 1% of the undertaking’s total worldwide annual turnover for the preceding financial year, whichever is higher.
These are regulatory penalty ceilings, not automatic penalties for every Authorised Representative or every compliance failure.
Actual enforcement depends on the circumstances of the infringement, the applicable national framework, and the relevant legal provisions.
For individuals acting as Authorised Representatives, potential personal, civil, or criminal liability must be assessed separately under the law of the relevant EU Member State.
6. Practical Risk Scenarios for Manufacturers and Authorised Representatives
Understanding potential operational scenarios can help both parties establish appropriate safeguards.
Scenario 1: Normal Compliance Operations
The manufacturer maintains accurate technical documentation, manages cybersecurity requirements, and provides the AR with the necessary information.
The AR maintains the required documents and responds to occasional regulatory requests.
This represents a relatively predictable operating model with limited administrative workload.
Scenario 2: Vulnerability or Regulatory Investigation
A cybersecurity vulnerability or potential non-conformity triggers an investigation or request for information.
The AR must coordinate with the manufacturer to obtain relevant technical evidence and respond appropriately.
Delayed or incomplete manufacturer responses can create operational difficulties for the AR, particularly when regulatory deadlines are involved.
Scenario 3: Serious Non-Conformity and Insufficient Cooperation
The manufacturer fails to provide reliable documentation or adequate support during a regulatory investigation.
If the AR also fails to perform its own mandated duties or provides misleading information, its conduct may become a separate regulatory concern.
This situation can result in increased legal costs, regulatory scrutiny, contractual disputes, and potential reputational consequences.
These scenarios highlight the importance of clear responsibilities, reliable documentation, and effective escalation procedures.
7. Key Considerations Before Appointing an Authorised Representative
Before entering into an AR arrangement, manufacturers and prospective representatives should establish several safeguards.
- Define the scope clearly: Identify the specific products and responsibilities covered by the mandate and ensure consistency with Article 18.
- Establish documentation procedures: Define how the manufacturer will provide and maintain access to the EU Declaration of Conformity, technical documentation, and relevant regulatory information.
- Agree on response and escalation processes: Establish clear communication channels and appropriate response times for market surveillance requests.
- Address incomplete or unreliable information: Define escalation procedures and contractual remedies where the manufacturer fails to provide necessary information.
- Review liability and insurance arrangements: Consider appropriate provisions for legal defence costs, professional liability insurance, indemnification, and termination.
For individual Authorised Representatives, independent legal advice concerning applicable national law is particularly important.
How CyberWhiz Can Help
At CyberWhiz, we support manufacturers in understanding and implementing the cybersecurity requirements of the EU Cyber Resilience Act.
While the appointment of an Authorised Representative is a regulatory and contractual decision, effective CRA readiness also depends on the manufacturer’s ability to demonstrate product cybersecurity compliance.
Our cybersecurity specialists can support manufacturers through:
- CRA Gap Analysis: Assessing existing product security practices against applicable CRA requirements.
- Cybersecurity Risk Assessment: Identifying and documenting risks across embedded devices, software, mobile applications, and cloud services.
- Technical Documentation Support: Preparing and organising cybersecurity evidence relevant to CRA conformity assessment and regulatory requests.
- Penetration Testing and Security Validation: Identifying vulnerabilities and evaluating the effectiveness of implemented security controls.
- Vulnerability Management: Supporting coordinated vulnerability disclosure, security issue triage, remediation tracking, and reporting readiness.
- Security Logging and Monitoring: Real-time embedded security and mobile application security protection during the lifecycle of the product.
- Supplier and Third-Party Risk Management: Assessing cybersecurity risks introduced by external components and service providers.
Our VDP Manager also supports manufacturers in managing vulnerability disclosure and handling workflows throughout the product lifecycle.
An Authorised Representative can support regulatory coordination, but CRA compliance starts with the manufacturer.
Contact [email protected] to discuss how CyberWhiz can support your organisation’s CRA readiness.
Regulatory References and Disclaimer
Regulatory references: Regulation (EU) 2024/2847, particularly Articles 13, 18, 28, 31 and 64.
Disclaimer: This article provides general regulatory information and does not constitute legal advice. Specific contractual arrangements, liability questions, and national enforcement requirements should be reviewed with qualified legal counsel.