
We Joined a Panel on CRA Reporting Obligations at The Things Conference
CyberWhiz joined the IoT Security Foundation panel at The Things Conference 2026 in Amsterdam to discuss the newly applicable Cyber Resilience Act (CRA) reporting obligations and what manufacturers need to do to be operationally ready for the new 24-hour reporting requirement.
CyberWhiz Joins IoT Security Foundation Panel on CRA Reporting Obligations at The Things Conference 2026
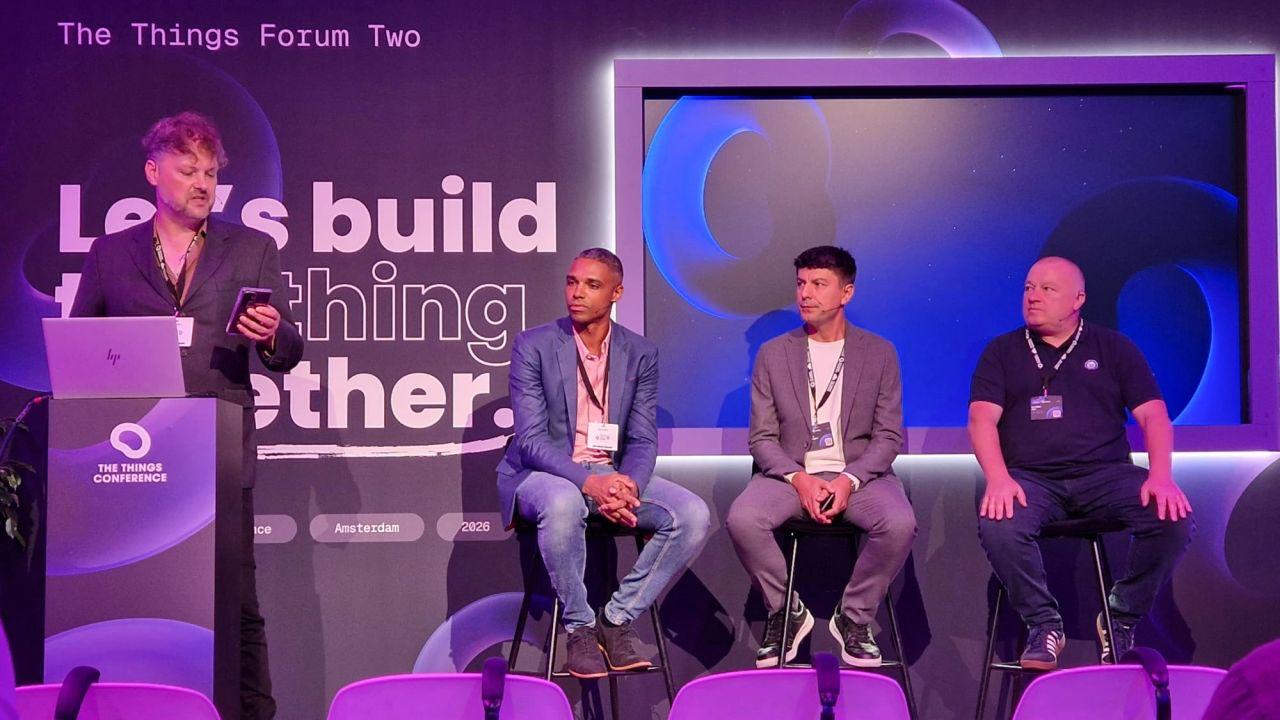
CyberWhiz took part in The Things Conference 2026, held in Amsterdam on 22-23 September, just days after the CRA reporting obligations became applicable on 11 September 2026.
Our Founder & CEO, Çağatay Büyüktopçu, joined the IoT Security Foundation panel “CRA Reporting Obligations”, moderated by Christopher Bennison from IoTSF, alongside David Nosibor from Red Alert Labs and Joe Lomako from TÜV SÜD.
The discussion focused on a key question for connected product manufacturers: what does it actually take to be ready to meet the CRA reporting obligations in practice?
Reporting Starts with Visibility
One of CyberWhiz’s key messages during the panel was that the CRA reporting requirements are no longer a future compliance issue.
With an initial early warning required within 24 hours after a manufacturer becomes aware of an actively exploited vulnerability or severe security incident affecting its product, companies cannot wait for an incident to start building their response process.
Manufacturers need visibility into their products, software components, versions and vulnerabilities before an incident occurs.
“Twenty-four hours is not enough time to build a process. It is only enough time to execute a process you already have.” — CyberWhiz